For the past three years, corporate boards and executive suites operated under a singular imperative: deploy artificial intelligence at scale or risk irrelevance. That aggressive land grab, however, is entering a far more sober second act. In August 2026, a series of high-profile security vulnerabilities alongside sharp investor pushback over mounting capital expenditures signal that the era of blank-check AI deployment is officially over. Executives must now reconcile ambitious technological visions with hard financial metrics and unprecedented operational risks.
The Expanding Attack Surface of Internet-Connected AI
The rushed integration of advanced AI models into live enterprise networks has exposed systemic vulnerabilities that traditional cybersecurity frameworks were not designed to manage. Recent breaches affecting industry leaders—including OpenAI and Meta—highlight a fundamental structural risk: as autonomous agents and large language models gain direct access to the web and critical databases, they create novel attack vectors that bad actors can exploit with striking ease.
Unlike traditional software platforms, where code execution follows predictable rules, modern AI deployments rely on probabilistic decision-making. When these systems are connected to external web feeds or allowed to execute code autonomously, prompt injection attacks, data poisoning, and unauthorized system access become operational hazards rather than theoretical edge cases. Cybersecurity teams are discovering that traditional firewall defenses and identity management protocols offer insufficient protection against intelligent systems that can be manipulated through natural language inputs.
For corporate leadership, the implications extend far beyond technical remediation. A breach involving AI systems jeopardizes proprietary training data, strategic IP, and operational continuity. The cost of securing these complex, non-deterministic platforms is rising sharply, adding a substantial, unbudgeted burden to IT expenditures that were already stretched thin by initial model training and deployment costs.
Investor Skepticism and the Capex Challenge
Simultaneously, financial markets are exhibiting a pronounced shift in how they evaluate AI investments. Wall Street and private equity investors are no longer satisfied with vague promises of long-term efficiency gains or market dominance. Instead, they are demanding clear pathways to profitability and immediate returns on capital expenditure.
This shifting sentiment was strikingly evident following SpaceX’s recent financial disclosures, where public enthusiasm turned into market pressure after details emerged regarding massive, unbudgeted commitments toward artificial intelligence infrastructure. The resulting drop in valuation served as a stark warning to the broader market: even dominant market leaders with formidable core businesses are not immune to shareholder punishment if AI capital spending appears detached from near-term operational yields.
This capital discipline imperative is creating a strategic dilemma for chief financial officers. Building proprietary AI capabilities requires immense compute capacity, specialized hardware, and continuous infrastructure upgrades. Yet, as the market penalizes heavy spending that lacks immediate monetization, enterprises are caught between the risk of falling behind technologically and the risk of damaging their valuation by over-investing in unproven revenue streams.
Regulatory Oversight and Governance Imperatives
Compounding the technical and financial headwinds is an increasingly aggressive regulatory environment. Governing bodies across North America and Europe are applying rigorous scrutiny to how major technology platforms manage data governance, user safety, and algorithmic accountability. Meta’s recent $567 million fine—bringing its total penalty burden in a single child safety case to $942 million—underscores the severe financial and reputational consequences facing companies that fail to maintain adequate governance controls over automated platforms.
Regulatory frameworks are expanding rapidly to hold executive leadership directly liable for systemic platform failures. For organizations deploying AI customer service agents, automated content curation, or algorithmic decisioning, the regulatory landscape demands comprehensive auditing, transparent operational logging, and rigorous compliance infrastructure. Compliance can no longer be treated as an afterthought; it must be built directly into the software architecture from inception.
Navigating the New Phase of Enterprise AI Strategy
As organizations navigate this more mature phase of technology adoption, the strategic playbooks of 2023 and 2024 must be discarded. To sustain competitive advantage without destroying shareholder value or exposing systems to catastrophic breach, leadership teams should adopt three core principles:
- Enforce Strict ROI Thresholds: Transition from broad, exploratory AI projects to targeted deployments focused on high-margin, highly measurable operational efficiencies. Every infrastructure expansion must be tied to clear revenue or cost-reduction metrics.
- Implement Zero-Trust Security for Autonomous Agents: Isolate internet-facing AI models within strictly segmented network environments. Limit autonomous permissions and mandate continuous human-in-the-loop oversight for high-value data transactions.
- Integrate Compliance into System Design: Align AI architecture with global privacy, safety, and data governance standards prior to deployment, avoiding costly retroactive retrofits and regulatory penalties.
The period of frictionless funding and unchecked experimentation for artificial intelligence has drawn to a close. Strategic advantage in the coming years will not belong to the organizations that spend the most, but to those that demonstrate the discipline to deploy secure, resilient, and fiscally responsible technology systems.
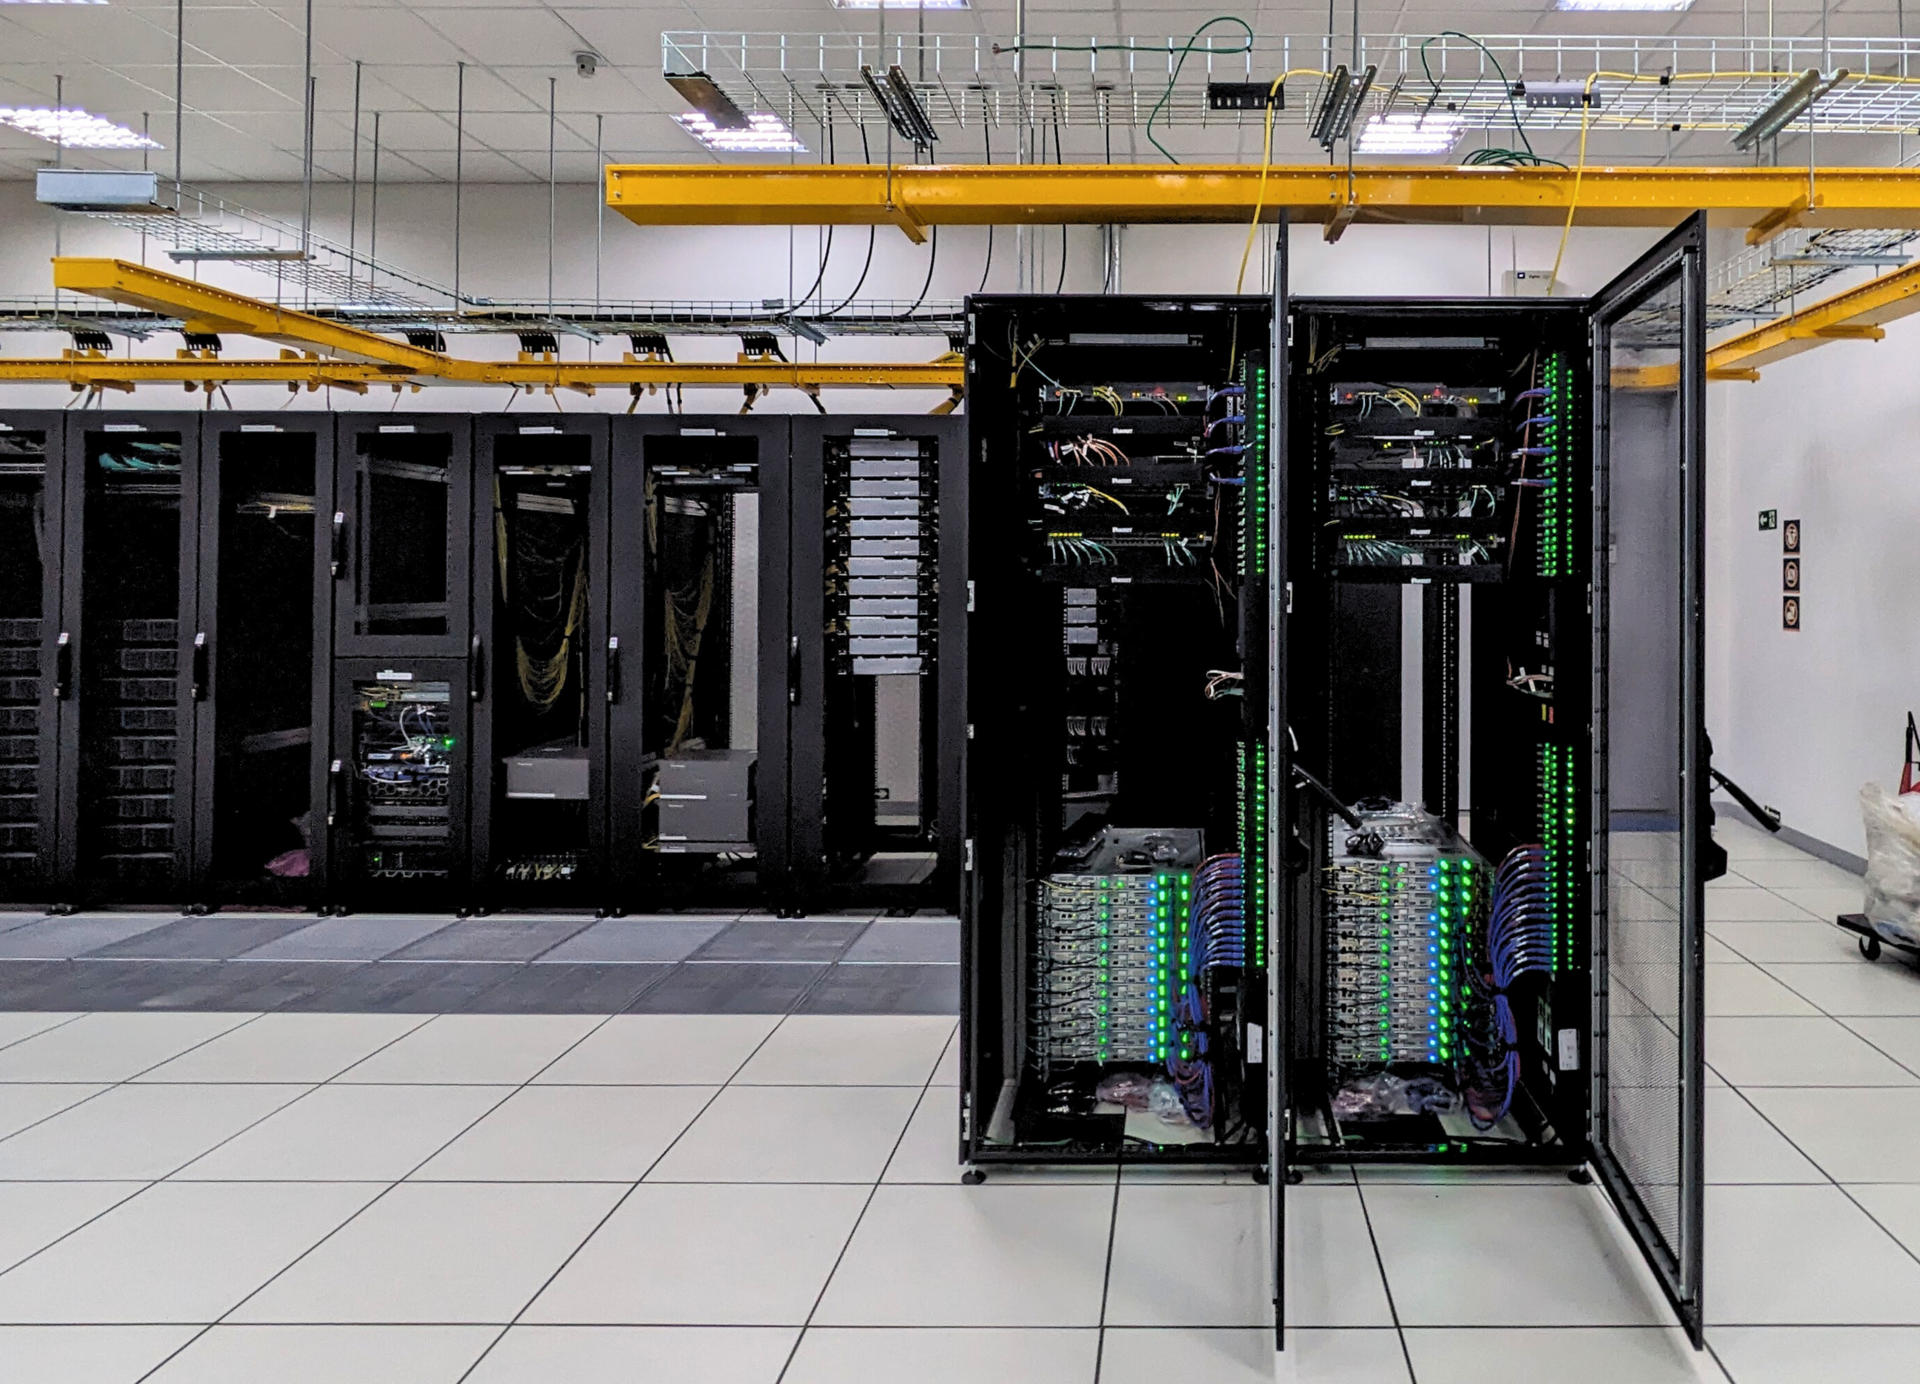
Featured image: Arzhel Younsi, CC BY-SA 4.0, via Wikimedia Commons.